How to Format and Validate JSON Without Leaking API Data
JSON is one of the easiest formats to copy around and one of the easiest formats to accidentally leak. Use a synthetic payload and verify the tool's input handling. Running a transformation locally does not prevent the page from loading analytics or advertising.
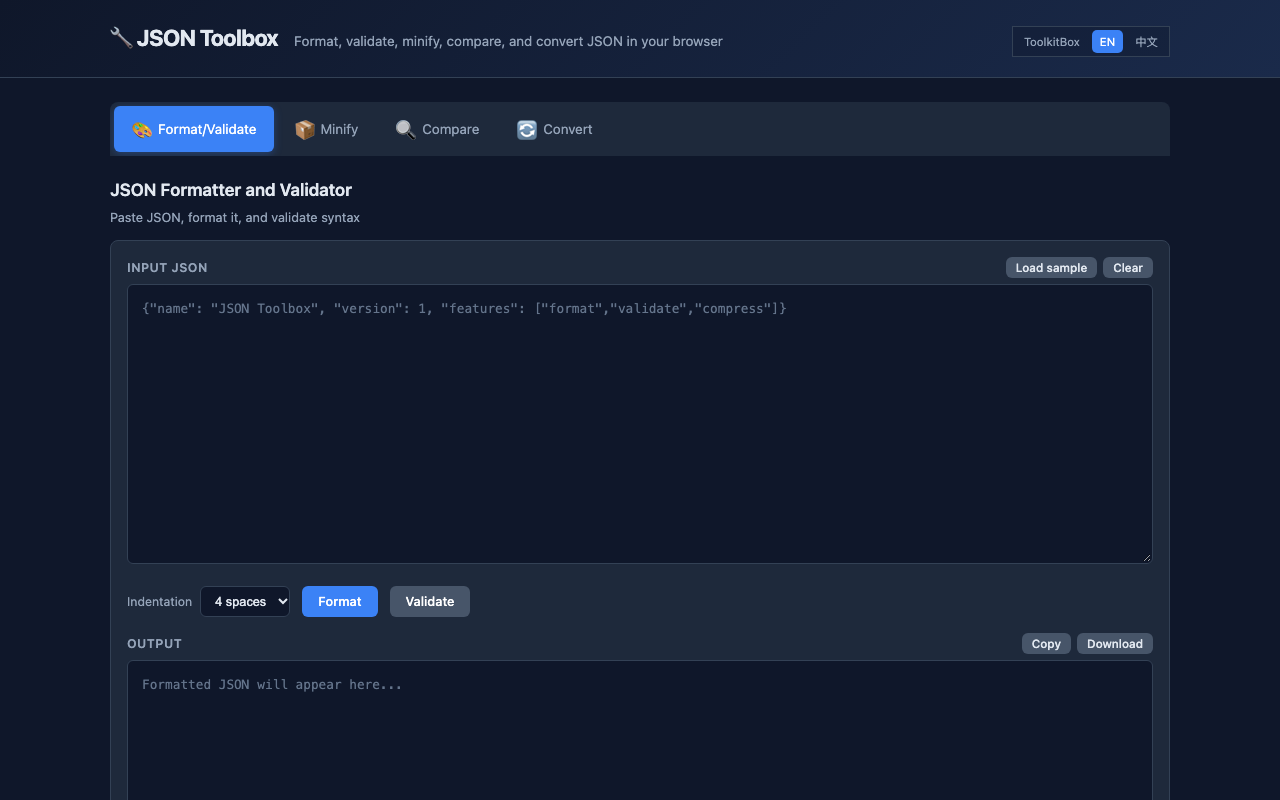
Start with validation before beautifying
When a JSON payload fails, the first question is whether the document is valid at all. Validate the syntax before making other changes. A missing comma, an extra trailing comma, or a mismatched quote can make downstream debugging feel much larger than it is. After validation passes, formatting makes nested objects easier to scan and review.
Use formatting to review structure, not just appearance
Pretty printing is useful because it exposes shape. You can see whether arrays are nested too deeply, whether a field appears at the wrong level, and whether an API response includes unexpected keys. This is especially helpful when debugging webhooks, third-party API responses, feature flags, and generated configuration.
Compare payloads when behavior changes
If a request worked yesterday but fails today, compare the previous payload against the current one. A diff can reveal renamed fields, missing optional properties, type changes, and null values that are hard to notice in a long response. For structured data, comparing formatted JSON is usually clearer than comparing one-line minified strings.
Convert only after cleaning the source
Conversions between JSON, YAML, and XML work best when the source is valid and predictable. Clean the JSON first, confirm the structure, and then convert. This reduces the chance of carrying a hidden syntax issue into another format where the error becomes harder to trace.
Keep sensitive data local
Do not paste production secrets, access tokens, private customer records, or confidential logs into a tool unless you understand where processing happens. ToolkitBox tools are built around local browser workflows where possible, which is the safer default for routine developer cleanup.
A reproducible validation workflow
- Copy only the smallest payload that reproduces the problem.
- Replace bearer tokens, cookies, emails, account IDs, names, URLs, and free-text fields with synthetic values.
- Validate syntax before formatting. Record the first parser error rather than changing several characters at once.
- Format the valid document, then inspect object boundaries, arrays, nulls, and value types.
- Compare the cleaned payload with the expected shape or a known-good fixture.
- Run schema or application validation after syntax validation; they answer different questions.
This order matters. Pretty-printed JSON can still be structurally wrong for an API, while a schema-valid document can still contain an unsafe real credential.
Example: isolate a syntax error without exposing production data
Suppose a webhook handler rejects a customer event. Reduce it to an invented fixture before testing:
{
  "event": "invoice.updated",
  "account_id": "TEST_ACCOUNT_001",
  "attempt": 2,
  "items": [
    {"sku": "DEMO-SKU", "quantity": 1}
  ]
}
If the original failure involved a trailing comma, preserve only that syntax condition in a separate failing fixture. Do not keep the customer's address, invoice notes, signed callback URL, or authorization header merely to make the sample look realistic.
JSON edge cases worth testing
- Missing, null, and empty: an absent key,
null, an empty string, and an empty array are four different states. - Numbers: very large integers can lose precision in JavaScript. Keep identifiers as strings when exact digits matter.
- Duplicate keys: parsers may silently retain the last value. Reject duplicates upstream when ambiguity would be dangerous.
- Unicode: visually identical text can use different code-point sequences. Test normalization when matching names or identifiers.
- Dates: JSON has no native date type. Validate timezone and format rules in application code or a schema.
- Encoded content: Base64 and escaped JSON strings can hide sensitive data. Decode and inspect them before sharing a fixture.
What this guide and tool do not prove
Syntax validation proves only that a parser can read the document. It does not prove that an API will accept the fields, that values are trustworthy, or that a payload is safe to log. JSON-to-YAML or JSON-to-XML conversion can also change typing, ordering expectations, or representation details. Review the destination format and test the receiving system with synthetic data.
Sources and review notes
This workflow follows the JSON grammar in RFC 8259 and the interoperability guidance in ECMA-404. The examples were created for this guide and contain no production data. Review methodology is documented in the ToolkitBox editorial policy.
Try the related tool
Open JSON Toolbox to apply this workflow in your browser.